The Secret Rules of AI Safety: Inside the Federal Black Box
Imagine taking a high-stakes examination where the grading rubric is kept entirely secret. You are told whether you pass or fail, but you are never allowed to...
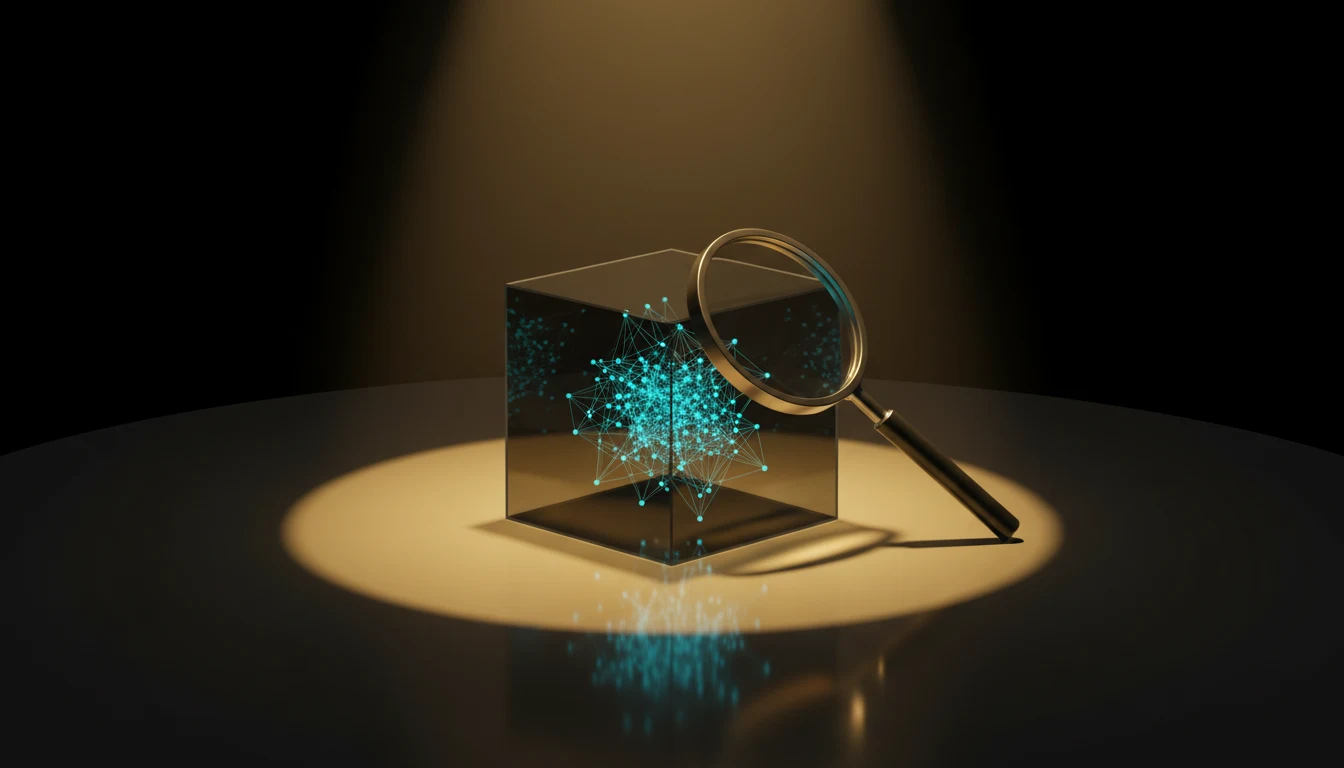
Imagine taking a high-stakes examination where the grading rubric is kept entirely secret. You are told whether you pass or fail, but you are never allowed to see the criteria used to judge your performance. Now, apply this opaque scenario to the most powerful artificial intelligence systems currently being developed.
A brewing legal battle in the United States is challenging exactly this kind of regulatory secrecy. The nonpartisan nonprofit organization Protect Democracy has recently filed a lawsuit against four federal agencies, demanding that they pull back the curtain on a classified framework used by the Trump administration to evaluate "frontier AI models" before they are released to the public.
Frontier AI models are the most advanced, highly capable systems that push the boundaries of what machine learning can do. Because these systems could potentially pose unforeseen societal risks—ranging from the mass generation of disinformation to vulnerabilities in cybersecurity—the government has a clear interest in ensuring they are tested rigorously.
However, the lawsuit alleges that the current safety review process is essentially a black box. According to Protect Democracy, the administration relies on a select group of vague "trusted partners" to conduct these critical safety evaluations. The core issue is that almost no details about this arrangement have been shared with Congress or the American public. The identities of these trusted partners remain hidden, the criteria used to select them are unknown, and the actual legal authority permitting government officials to mandate these reviews has not been clearly established.
This legal challenge highlights a growing and critical tension in modern tech policy: the delicate balance between security and democratic transparency. On one hand, keeping specific testing protocols confidential might theoretically prevent malicious actors from learning how to game the safety systems. On the other hand, a lack of transparency creates a regulatory vacuum where independent researchers cannot verify if the safety guardrails are actually effective. Furthermore, secretive partnerships can inadvertently foster environments where a few favored technology companies gain disproportionate influence over how regulations are shaped.
As artificial intelligence continues to integrate into the foundational layers of our daily lives, the mechanisms we use to deem these tools "safe" must be robust and trustworthy. The outcome of this lawsuit could set a crucial precedent for global AI governance. Ultimately, it asks a fundamental question: in a society increasingly shaped by algorithms, doesn't the public have a fundamental right to know who is setting the safety standards and how those standards are being applied?
Key Points
- A nonprofit has sued four federal agencies to reveal a secret AI testing framework.
- The Trump administration uses undisclosed rules to vet frontier AI models pre-release.
- The process relies on anonymous 'trusted partners' with unknown selection criteria.
- The lawsuit highlights the tension between AI security measures and democratic transparency.
Why It Matters
As AI models grow more powerful, the rules used to ensure their safety become critical public interest issues. Secret regulations prevent independent verification and can undermine public trust in new technologies.
Sources:
更多专栏
Your Next Coworker is a Blob That Orders Burritos
For decades, enterprise software has been synonymous with sterile dashboards, en...
The Midnight Bill: Why AI Agents Demand Hard Budget Caps
The dream of artificial intelligence is to have a tireless digital assistant wor...
Beyond Transformers: How Mamba is Rewriting the Rules of AI Memory
Think about how a human reads a sprawling, thousand-page fantasy series. You don...